ina RKI
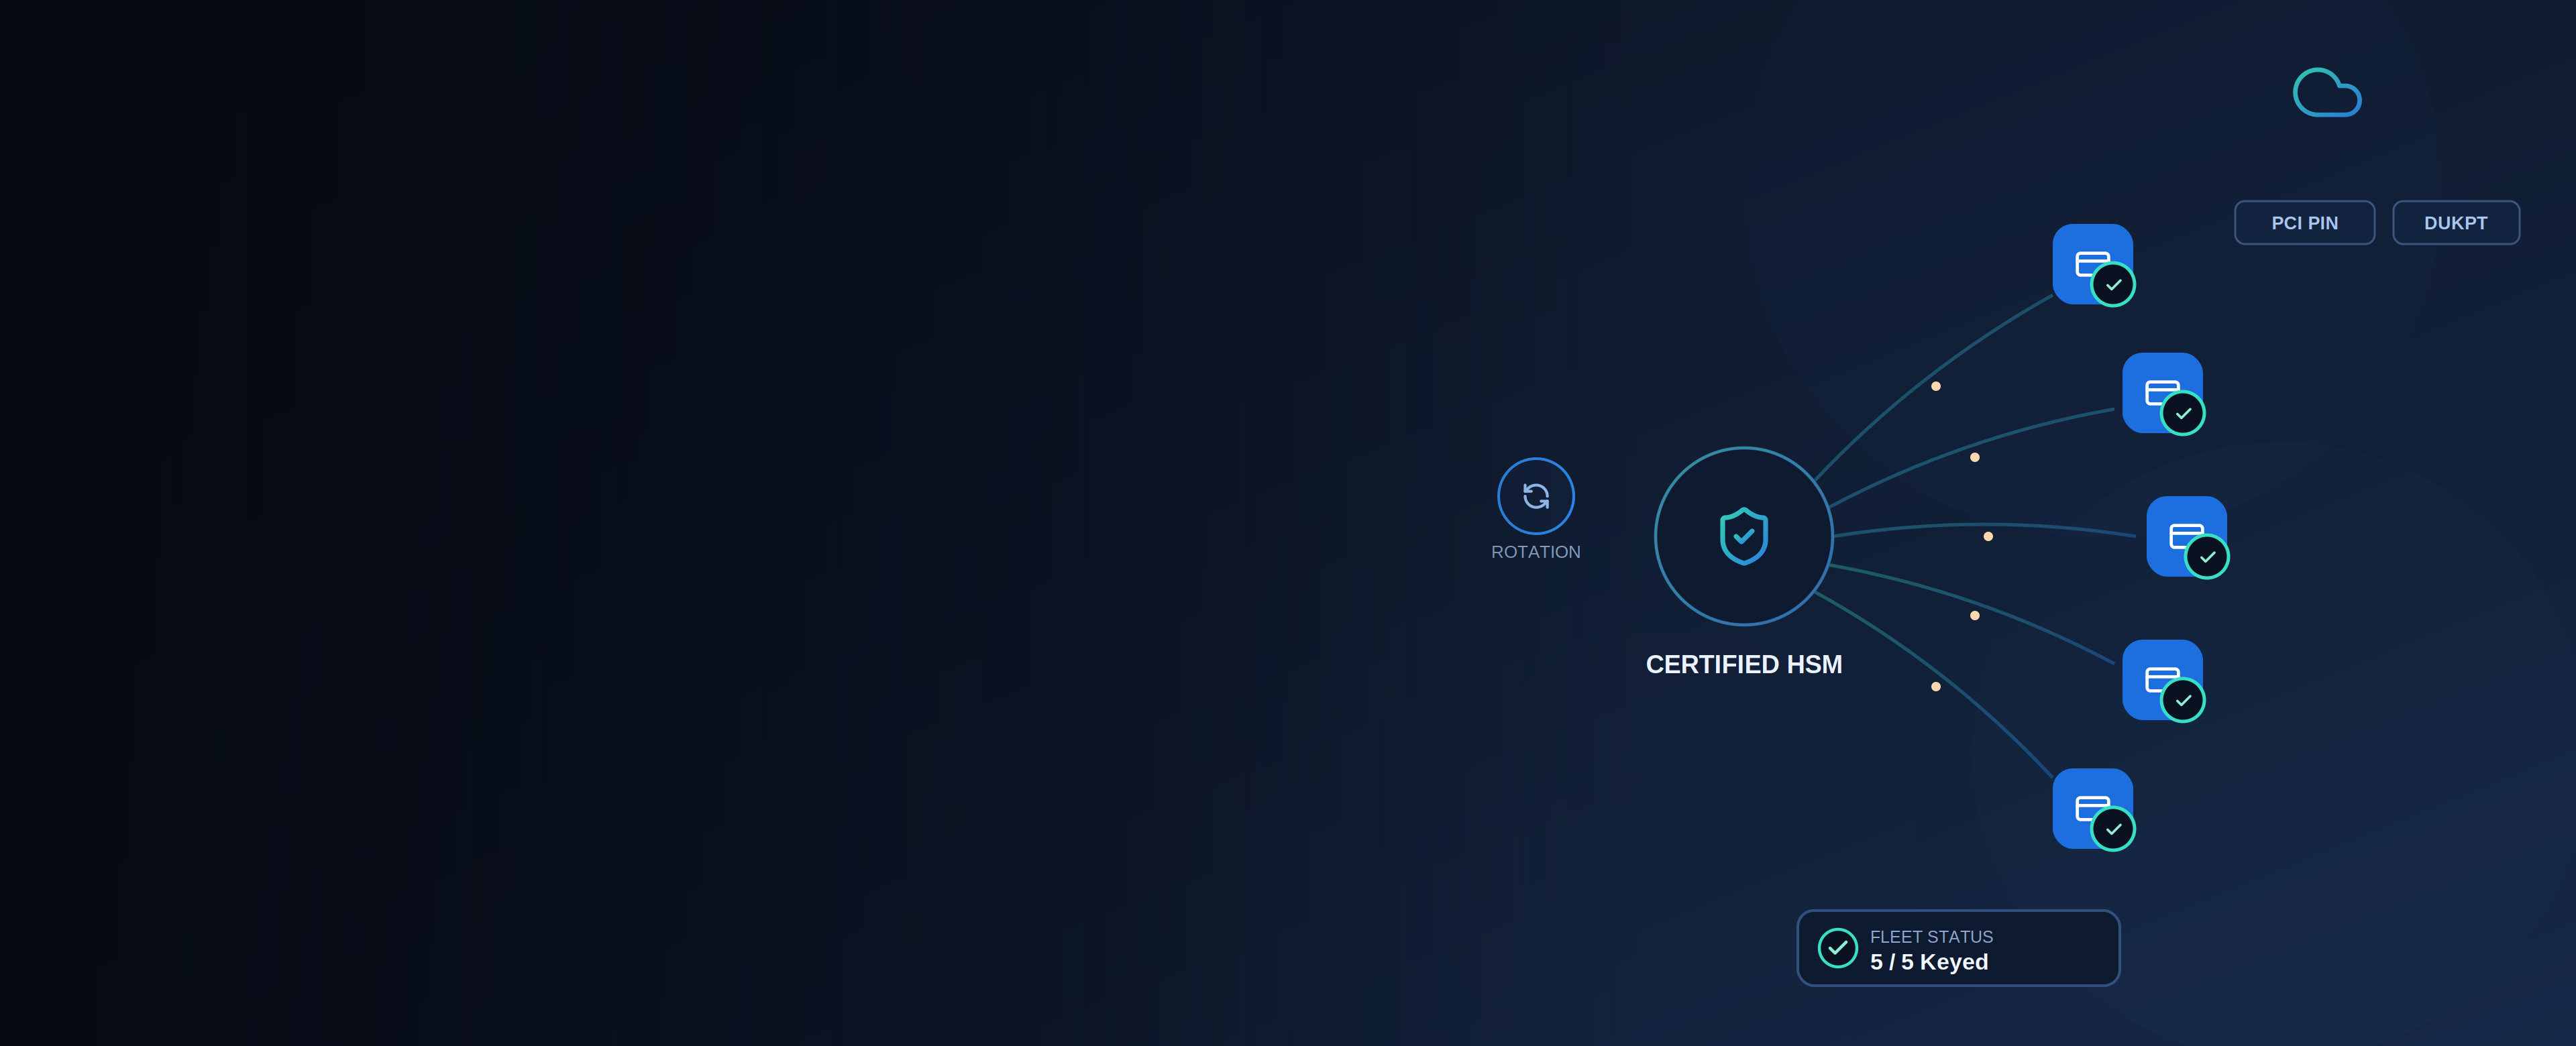
ina RKI generates, injects, distributes and rotates encryption keys across a terminal fleet entirely remotely, every key born and wrapped inside a certified HSM, delivered to the device over a secure channel, with no technician ever needing to open a terminal or load a key locally. The same HSM-backed infrastructure also handles data encryption for sensitive cardholder information and PIN translation as transactions move between networks.
Platform Architecture Overview
ina RKI sits between the HSM where keys are born and the terminal fleet that needs them. It generates and wraps keys inside certified secure hardware, pushes them to terminals over an authenticated channel, and keeps a complete record of every injection, rotation and expiry, so a merchant's key estate is never a black box. The same HSM infrastructure also encrypts sensitive data and translates PIN blocks between network zone keys, so key management, data protection and PIN handling all run on one secure hardware foundation instead of three disconnected systems.
 HSM Integration & Secure Channels
 Key Generation & Injection Workflow
 Key Distribution & Sync with Terminals
 Key Expiry Tracking & Rotation Scheduling
 Key Audit Trails & Compliance Logs
 Data Encryption Services
 PIN Translation
Generation Layer
Distribution Layer
Lifecycle Layer
Data Protection Layer
Compliance Layer
End-to-End Platform Architecture
From key ceremony to a terminal ready to process, one controlled key lifecycle
1. Key Ceremony
Keys are generated inside a certified HSM under dual control, so a clear-text key value never exists outside secure hardware.
2. Key Wrapping
Generated keys are wrapped for secure transport, using DUKPT derivation or a master key / session key scheme depending on what the acquirer or scheme requires.
3. Secure Channel Injection
The wrapped key is pushed to the target terminal over an authenticated, encrypted channel, remotely, with no technician needed to open the device or attach a local key-loading tool.
4. Distribution & Sync
Keys are synced across the relevant terminal fleet, matched to the correct merchant, store and device profile.
5. Rotation Scheduling
Keys rotate on a policy-driven schedule tied to their expiry, or on demand, keeping the estate inside its compliance window instead of drifting past it.
6. Revocation
A lost, stolen or decommissioned terminal can have its keys revoked immediately, cutting it out of the estate without touching any other device.
7. Audit & Compliance Logging
Every ceremony, injection, rotation and revocation is logged, giving assessors and internal compliance teams a record they can actually review.
Core Technical Capabilities
HSM-backed key generation, remote injection, rotation and data protection controls
HSM-Backed Key Generation
Every key is generated inside a certified hardware security module under dual control, so a clear key value never exists outside secure hardware, not during generation, not in transit.
DUKPT and Master Key / Session Key Support
Supports both DUKPT derivation and traditional MK-SK schemes, so ina RKI fits whichever key management model a given network or acquirer already requires, instead of forcing a single approach.
Fully Remote Injection
Keys reach terminals over a secure channel with no technician visit and no local key-loading device required, cutting rollout time and field cost for every terminal added to the fleet.
Policy-Driven Rotation
Rotation runs on a schedule tied to key expiry policy, or can be triggered on demand, so no terminal quietly keeps running on a key that is past its compliance window.
Instant Revocation
A lost, stolen or decommissioned terminal's keys can be revoked immediately, isolating that one device without disrupting the rest of the fleet.
Complete Audit Trail
Every key ceremony, injection, rotation and revocation is logged, giving PCI assessors and internal compliance teams a record they can review instead of reconstructing key history from scattered notes.
PIN Translation Without Exposing the Clear PIN
As a transaction moves from one network or acquirer to another, its PIN block is decrypted under the sending zone's key and re-encrypted under the receiving zone's key, entirely inside the HSM, so the clear PIN is never exposed outside secure hardware at any translation hop.
End-to-End Data Encryption on the Same HSM Infrastructure
Sensitive cardholder and account data is encrypted using the same HSM-backed key infrastructure that handles terminal keys, so data protection doesn't require a separate, disconnected encryption system to manage and audit.
Extended Capabilities
Advanced controls for secure key lifecycle and data protection

Dual Control Key Ceremonies

Secure Key Block Wrapping for Transport

Multi-Acquirer / Multi-Scheme Key Profiles

Terminal Fleet Key Status Dashboard

Expiry Alerts Before Compliance Windows Close

Emergency Mass Revocation
Who Integrates With the Platform
Key management infrastructure for every participant in the terminal lifecycle
Acquirers and PSPs
Roll out and rotate keys across an entire merchant estate without dispatching a technician for every terminal, and keep the whole fleet inside its compliance window from one system.
POS and Terminal OEMs
Build remote key injection into device provisioning, so every terminal leaves the factory or warehouse ready to be keyed remotely instead of requiring a manual load before deployment.
Merchants and Retail Chains
Multi-location merchants keep every terminal's keys current and compliant from one dashboard, no store visit required for a routine rotation.
Compliance and PCI Assessment Teams
Get a ready-made audit trail of every key event instead of reconstructing key history from scattered logs and field paperwork during an assessment.
Platform Facts
How ina RKI secures key management and data protection across the terminal estate
Zero Clear-Text Key Exposure
Keys are generated and wrapped inside a certified HSM and never exist in the clear outside secure hardware, at any stage of the lifecycle.
Two Key Models Supported
Both DUKPT derivation and traditional master key / session key schemes are supported, so onboarding doesn't depend on the acquirer standardizing on one model.
Built Into the TMS Platform, Available Standalone
Originally delivered as the Remote Key Loading module inside ina's Terminal Management System, now available as its own solution for teams that need key management without adopting the full TMS.
White Label or SaaS Deployment
Available white label, deployed in a client's own environment with full ownership, or as a SaaS subscription on shared secure cloud infrastructure, the same delivery flexibility used across the rest of the platform.
Full Audit Trail by Design
Every key ceremony, injection, rotation and revocation is logged from day one, not bolted on before an assessment.
FAQ
How does ina RKI prevent an encryption key from ever existing in clear text outside the HSM?
What's the actual difference between remote key injection and traditional local key loading?
Does ina RKI support DUKPT, or only traditional master key / session key schemes?
How fast can a compromised or stolen terminal's keys be revoked?
Does adopting ina RKI mean replacing our existing TMS or buying new terminals?
Can ina RKI translate PIN blocks between different network zone keys?
Partner With Us
Customer Trust Built on Global Reach and Consistent Reliability
0+
OEMs Partnered
0+
Countries
0+
PSPs Partnered